
We read your photo as:
What are the four key components of a threat and risk assessment for a CPO?
Business/Management
ScanSolve AI Answer
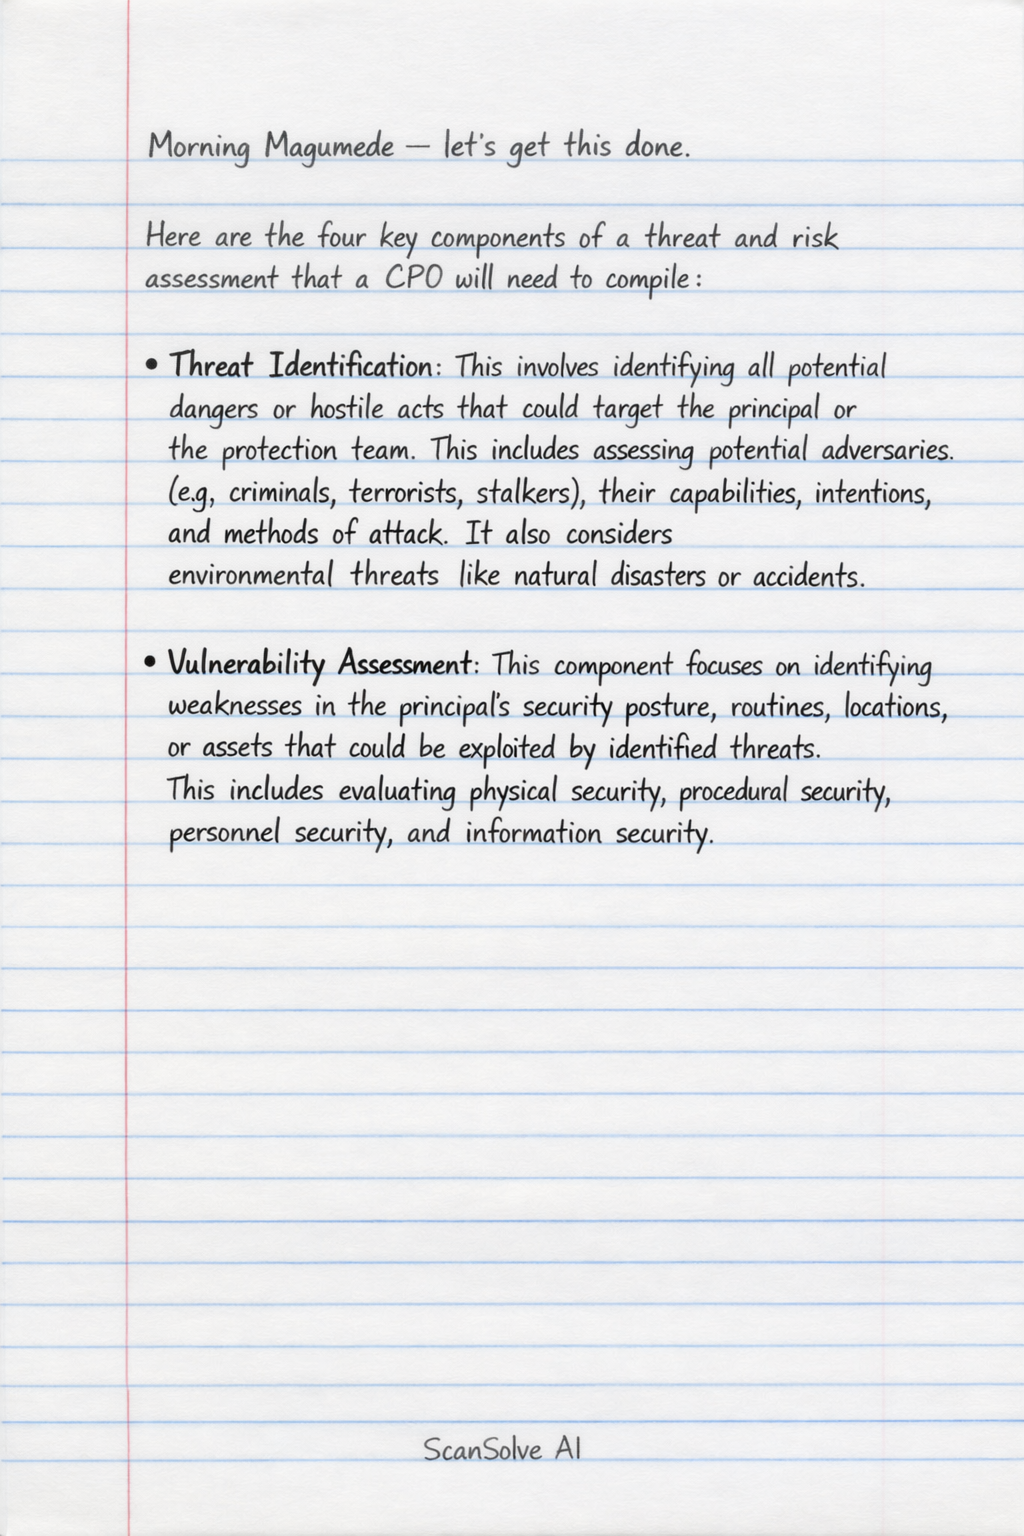
Here are the four key components of a threat and risk assessment that a CPO will need to compile:
- Threat Identification: This involves identifying all potential dangers or hostile acts that could target the principal or the protection team. This includes assessing potential adversaries (e.g., criminals, terrorists, stalkers), their capabilities, intentions, and methods of attack. It also considers environmental threats like natural disasters or accidents.
- Vulnerability Assessment: This component focuses on identifying weaknesses in the principal's security posture, routines, locations, or assets that could be exploited by identified threats. This includes evaluating physical security, procedural security, personnel security, and information security.
- Risk Analysis and Evaluation: This step involves assessing the likelihood of each identified threat exploiting a vulnerability and the potential impact if such an event occurs. Risks are typically categorized by severity (e.g., low, medium, high) and probability, allowing the CPO to prioritize which risks require the most attention.
- Mitigation and Countermeasures: Based on the risk analysis, this component outlines specific strategies, procedures, and resources to reduce or eliminate identified risks. This includes implementing security measures, developing emergency response plans, establishing protective protocols, and training personnel to minimize vulnerabilities and deter threats.
Was this helpful?
Still stuck on this one?
Ask a follow-up, and the answer starts from this question.
Got a different question?Ask your own question
More Business/Management Questions
QWhat aspects should be included in the 'nature and scope of the position' section of a job…QWhat are the key factors to consider when reviewing and updating CBPP contingency plans?QAnalyze Jack's CPO failures, their impact on the principal's comfort and trust, and indirectly…QIdentify and discuss four specific areas of Jack's conduct that failed to meet professional CPO…QDescribe the four critical elements for communication when used as a tool for preventive enforcement…
Handwritten Step-by-Step Solution
Get this as a handwritten image on WhatsApp — like a tutor wrote it for you.
Try on WhatsApp