
We read your photo as:
List the port number and service for each of the following: FTP, SSH, Telnet, SMTP, DNS, HTTP, POP3, HTTPS, MySQL, RDP.
Computer Science
ScanSolve AI Answer
Here's a summary of the essential port numbers and types of port scans:
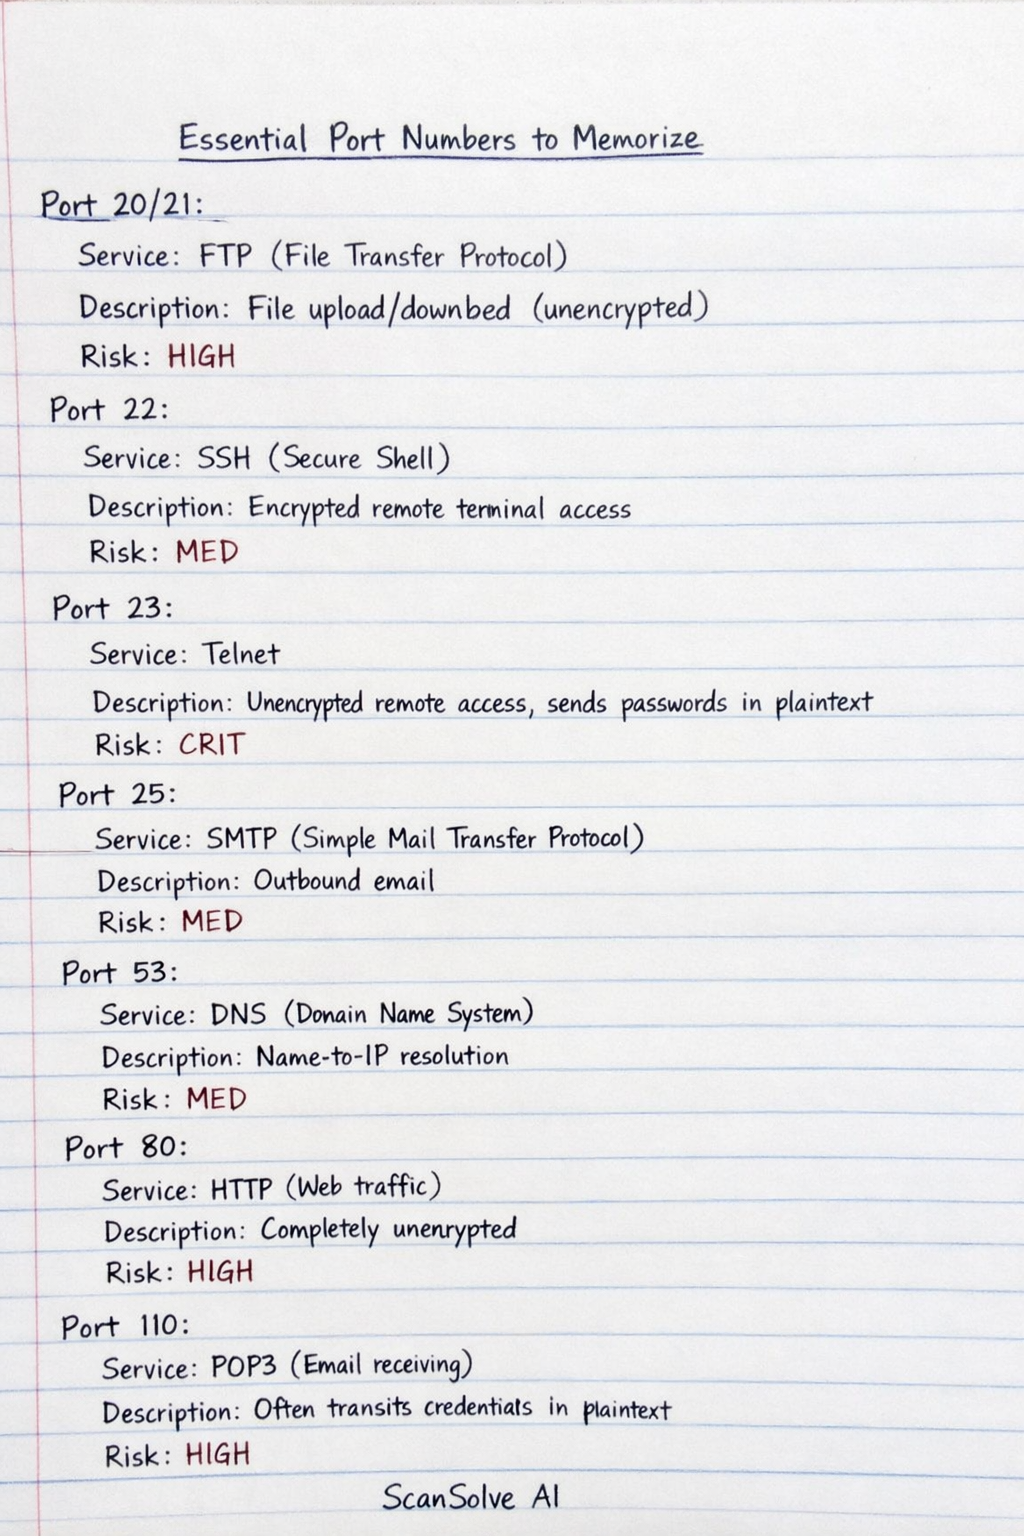
Essential Port Numbers to Memorize
- Port 20/21:
- Service: FTP (File Transfer Protocol)
- Description: File upload/download (unencrypted)
- Risk: HIGH
- Port 22:
- Service: SSH (Secure Shell)
- Description: Encrypted remote terminal access
- Risk: MED
- Port 23:
- Service: Telnet
- Description: Unencrypted remote access, sends passwords in plaintext
- Risk: CRIT
- Port 25:
- Service: SMTP (Simple Mail Transfer Protocol)
- Description: Outbound email
- Risk: MED
- Port 53:
- Service: DNS (Domain Name System)
- Description: Name-to-IP resolution
- Risk: MED
- Port 80:
- Service: HTTP (Web traffic)
- Description: Completely unencrypted
- Risk: HIGH
- Port 110:
- Service: POP3 (Email receiving)
- Description: Often transmits credentials in plaintext
- Risk: HIGH
- Port 443:
- Service: HTTPS (Encrypted web traffic)
- Description: TLS/SSL secured
- Risk: LOW
- Port 3306:
- Service: MySQL
- Description: MySQL database, should NEVER be internet-facing
- Risk: CRIT
- Port 3389:
- Service: RDP (Remote Desktop Protocol)
- Description: Windows remote access
- Risk: CRIT
Types of Port Scans
- Flag: -sT
- Scan Type: Connect Scan
- Stealth: LOW
- How it works: Completes the full TCP handshake. Most reliable but easily detected in server logs.
- Flag: -sS
- Scan Type: SYN / Half-Open
- Stealth: HIGH
- How it works: Sends SYN, receives SYN/ACK but never completes with ACK. Fewer logs. Most common scan.
- Flag: -sF
- Scan Type: FIN Scan
- Stealth: HIGH
- How it works: Sends FIN packet. Open ports ignore it; closed ports reply RST. Bypasses some firewalls.
- Flag: -sN
- Scan Type: NULL Scan
- Stealth: HIGH
- How it works: Sends a packet with NO flags set. Very stealthy against older or non-standard systems.
- Flag: -sX
- Scan Type: XMAS Scan
- Stealth: HIGH
- How it works: Sets FIN+PSH+URG flags simultaneously - 'lights up like a Christmas tree'. Very stealthy.
- Flag: -sA
- Scan Type: ACK Scan
- Stealth: MED
- How it works: Maps firewall rules - does NOT identify open ports, but reveals filtered vs. unfiltered.
- Flag: -sI
- Scan Type: Idle / Zombie
- Stealth: MAX
- How it works: Uses a third-party zombie machine's IP to probe target. Hides attacker identity completely.
Was this helpful?
Still stuck on this one?
Ask a follow-up, and the answer starts from this question.
Got a different question?Ask your own question
More Computer Science Questions
QIdentify the ports below and include the power ports USB port Game port HDMI port TRS port VGA port…QWhat are the different types of computers and their characteristics, including examples and port…QIdentify the types of servers and list their rolesQPrinters, files, and e-mail can all be categorized as Office equipment, Peer-to-peer networking…QWhat are the answers to the following multiple choice computer networking and software questions?
Handwritten Step-by-Step Solution
Get this as a handwritten image on WhatsApp — like a tutor wrote it for you.
Try on WhatsApp